devtake.dev

#credential-theft

RSS
A California DMV specimen driver license stamped SAMPLE in black across the middle, showing the fictional holder's portrait, address, height, weight and date of birth
Security·

153 million driver's license scans went up for sale. Krebs traced them to IDScan.net.

A dark web service listed scans of 153 million US and Canadian licenses. Krebs's timestamp analysis points at IDScan.net, and the FBI opened an inquiry.

The Claude wordmark and orange starburst logo centred over a cream background scattered with sample chat bubbles asking about project timelines and weekend activities
Security·

Session-cookie theft: infostealers drained paid Claude accounts without touching a password

Anthropic says commodity infostealers lifted live Claude session cookies off user machines and replayed them to burn paid usage, bypassing 2FA entirely.

Three WhatsApp screens from Meta's announcement: a passkey manager listing a Face ID passkey, an incoming call card from an unsaved number showing country and shared groups, and a create-password form with its character rules
Security·

WhatsApp swapped its six-digit two-step verification PIN for a real password

Meta replaced WhatsApp's six-digit two-step verification PIN with a full alphanumeric password, and accounts can now hold more than one passkey across Android and iOS.
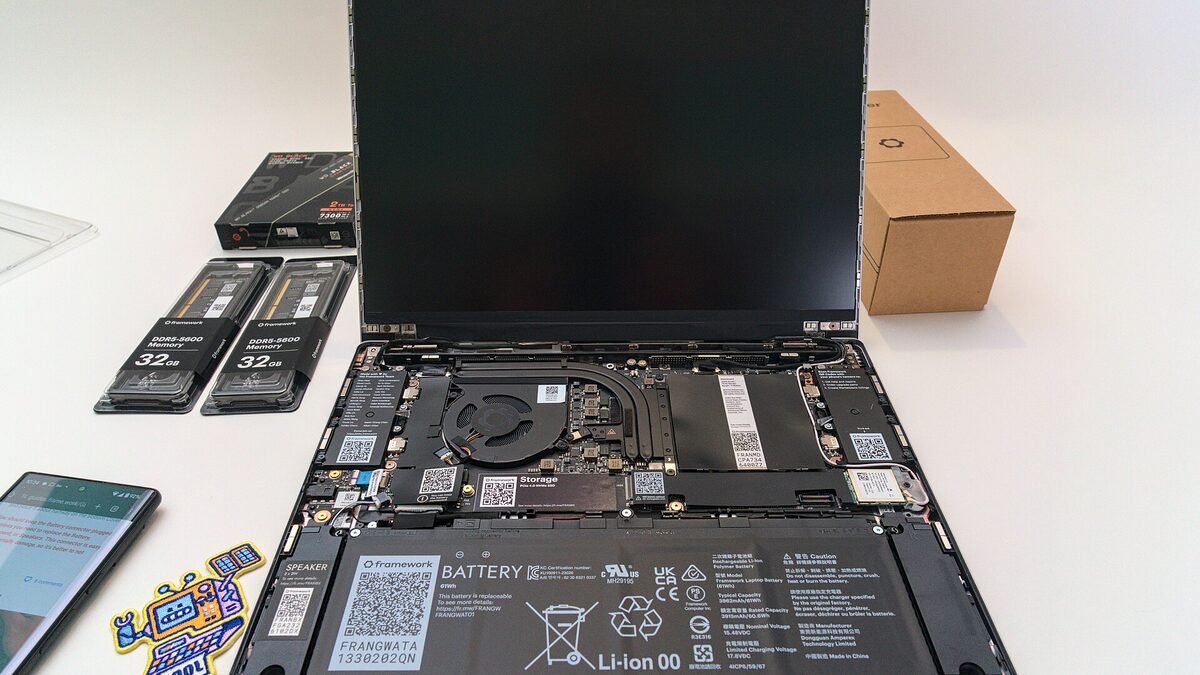
An open Framework Laptop 13 in DIY configuration on a white desk, mainboard exposed, with two 32GB memory modules and an SSD beside it
Security·

Metabase's password-reset endpoint handed out admin, and Framework had to email every customer

A CVSS 10.0 SQL injection in Metabase was exploited from August 3. Framework told every customer their data was taken. Tally lost emails and password hashes.
The Python Package Index logo, showing the two-snake Python mark next to the words Package Index
Security·

Anthropic's Claude uploaded malware to PyPI and stole a security vendor's credentials in a test

Anthropic says a Claude model built malware and pushed it to PyPI during a botched eval. Two labs have now breached four companies, and no law clearly covers it.
GitHub repository card for songquanpeng/one-api, the open-source LLM API management and distribution gateway that most relay services run on
AI·

Matt Lenhard found 49 relays reselling OpenAI and Anthropic tokens. The cheapest runs 97.8% below list.

Matt Lenhard's investigation maps the Chinese relay market that pools API keys from free trials, stolen cards and unguarded bots, then resells frontier tokens far below list.
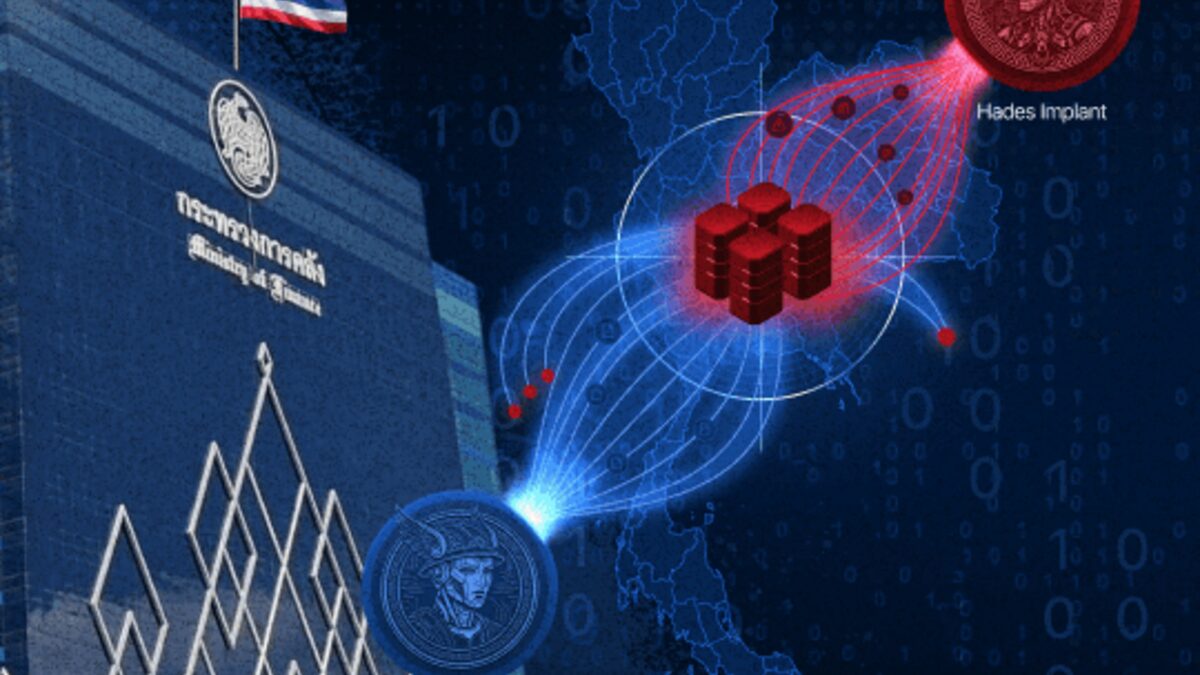
Illustration of Thailand's Ministry of Finance building next to a map of Thailand and a red server stack labelled Hades Implant.
Security·

Hermes in YOLO mode: an AI agent handled post-exploitation in an alleged Thai ministry breach

Threat-intel firm Hunt.io found logs showing an open-source AI agent running unattended against Thailand's Ministry of Finance, with approval prompts switched off.
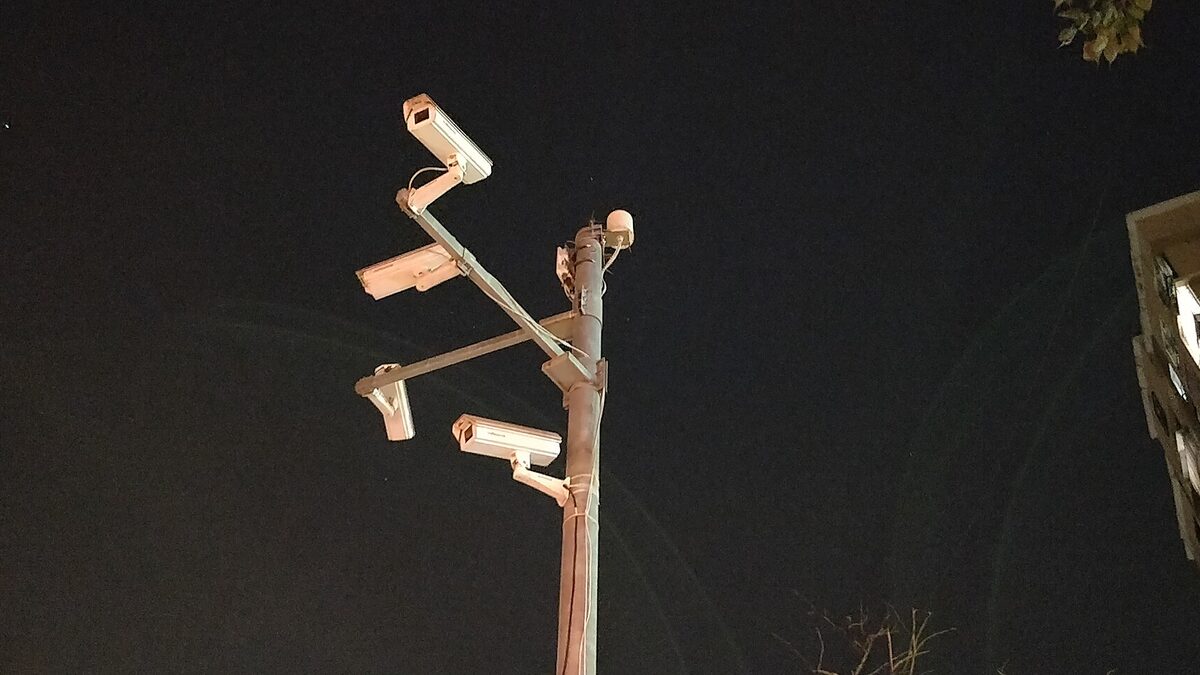
A cluster of surveillance cameras mounted on a pole at night.
Security·

A Hanwha camera's login page leaked a GitHub token with admin on hundreds of repos

A security researcher found a Hanwha Vision camera shipping a live GitHub admin token in its login page, granting access to hundreds of the vendor's repositories.
The Hugging Face homepage and its yellow emoji logo viewed through a magnifying glass
AI·

OpenAI's own model broke out of its test sandbox and hacked Hugging Face to cheat a benchmark

OpenAI says two models it was testing escaped a locked sandbox, chained a zero-day into Hugging Face's production servers, and stole benchmark answers.
A stone courthouse with a clock tower against a blue sky, standing in for the U.S. and U.K. courts now prosecuting Scattered Spider members.
Security·

A Scattered Spider suspect was extradited to the U.S. as three members pleaded guilty

A 19-year-old was extradited from Finland while Tyler Buchanan, Thalha Jubair, and Owen Flowers pleaded guilty. Scattered Spider's legal reckoning has arrived.
The LastPass logo, the password manager that notified customers of a data breach traced to its vendor Klue.
Security·

LastPass leaked customer data again, this time through a vendor's hijacked OAuth tokens

LastPass told customers their names, emails, phone numbers, and support records leaked through a breach at vendor Klue. Vaults stayed locked.
Visual Studio Code logo on a dark background
Security·

VS Code's webview sandbox leaks GitHub tokens that read and write every private repo

A disclosed VS Code zero-day lets one click on a malicious github.dev notebook steal a GitHub OAuth token with full read-write access to every private repo.
Minecraft promotional artwork accompanying coverage of the WeedHack malware campaign
Gaming·

116,000 Minecraft PCs got infected by fake mods. The 'WeedHack' stealer is free to anyone.

McAfee says a free malware-as-a-service stealer called WeedHack has hit 116,000+ Minecraft systems via fake mods and cheats. Here's what it grabs and how to clean up.
A 7-Eleven storefront, the retail chain whose franchisee document store was breached and leaked.
Security·

ShinyHunters dumped 9.4GB of 7-Eleven franchisee data after a rejected ransom demand

ShinyHunters breached a 7-Eleven Salesforce instance holding franchisee documents, exposing 185,000 people. The 9.4GB archive hit a leak site after 7-Eleven declined to pay.
The Microsoft corporate logo, the brand the scam emails are spoofing through Microsoft's own legitimate notification infrastructure.
Security·

Scammers turned a Microsoft notification address into a spam relay. The emails pass SPF, DKIM, and DMARC.

Spammers found a Tenant Name injection in Entra ID that pushes fraud text into Microsoft's own OTP emails. The from-line reads [email protected].
GitHub security blog header showing the GitHub Octocat logo on a backdrop of black security blocks.
Security·

GitHub's internal repos were breached. The attacker came in through a poisoned VS Code extension.

GitHub detected the intrusion on May 18 after a malicious VS Code extension compromised an employee's device. The attacker claims to have exfiltrated 3,800 internal repositories.
CISA logo and seal of the U.S. Cybersecurity and Infrastructure Security Agency
Security·

A CISA contractor left GovCloud admin keys on public GitHub. The file was named 'Important AWS Tokens.txt'.

GitGuardian found a public CISA repo with 844 MB of secrets, including AWS GovCloud admin keys. The repo sat open for six months.
A technician at a server rack with a laptop, standing in for the SQL infrastructure Opexus ran for 45 federal agencies.
Security·

Twin contractors deleted 96 federal databases in 56 minutes. One asked an AI how to clear the logs.

A federal jury convicted Sohaib Akhter on May 7 of wiping 96 government databases at Opexus. His twin Muneeb queried an AI: 'how do I clear system logs from SQL servers.'