
Security·
153 million driver's license scans went up for sale. Krebs traced them to IDScan.net.
A dark web service listed scans of 153 million US and Canadian licenses. Krebs's timestamp analysis points at IDScan.net, and the FBI opened an inquiry.
Supply-chain attacks, typosquatting, dependency compromises, and the ecosystem response.
A dark web service listed scans of 153 million US and Canadian licenses. Krebs's timestamp analysis points at IDScan.net, and the FBI opened an inquiry.

Alon Hertz registered package names that corporate docs told AI agents to install. Claude, Codex and Hermes fetched and ran the code within the hour.

Taiwan's Keelung prosecutors charged nine people, including an Nvidia Taiwan manager and two Supermicro sales managers, over 74 B300 servers that reached China.
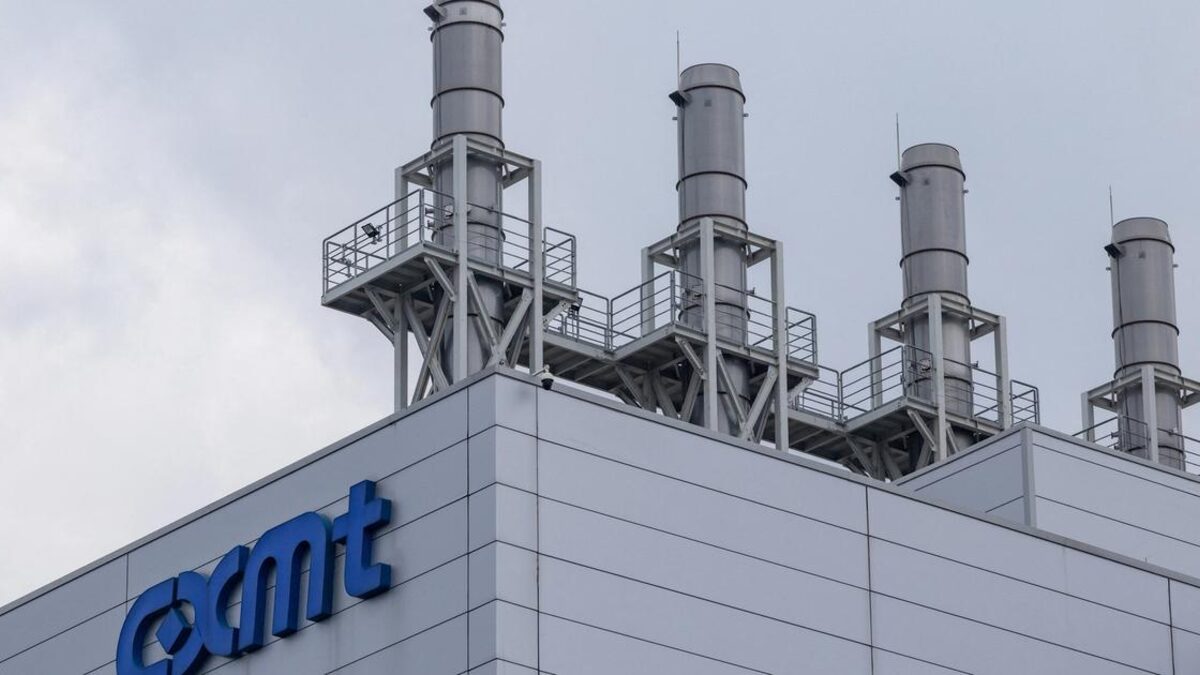
The Wall Street Journal says Apple is qualifying CXMT DRAM for iPhones and MacBooks. Export rules bar the spec work Apple normally does with a supplier.
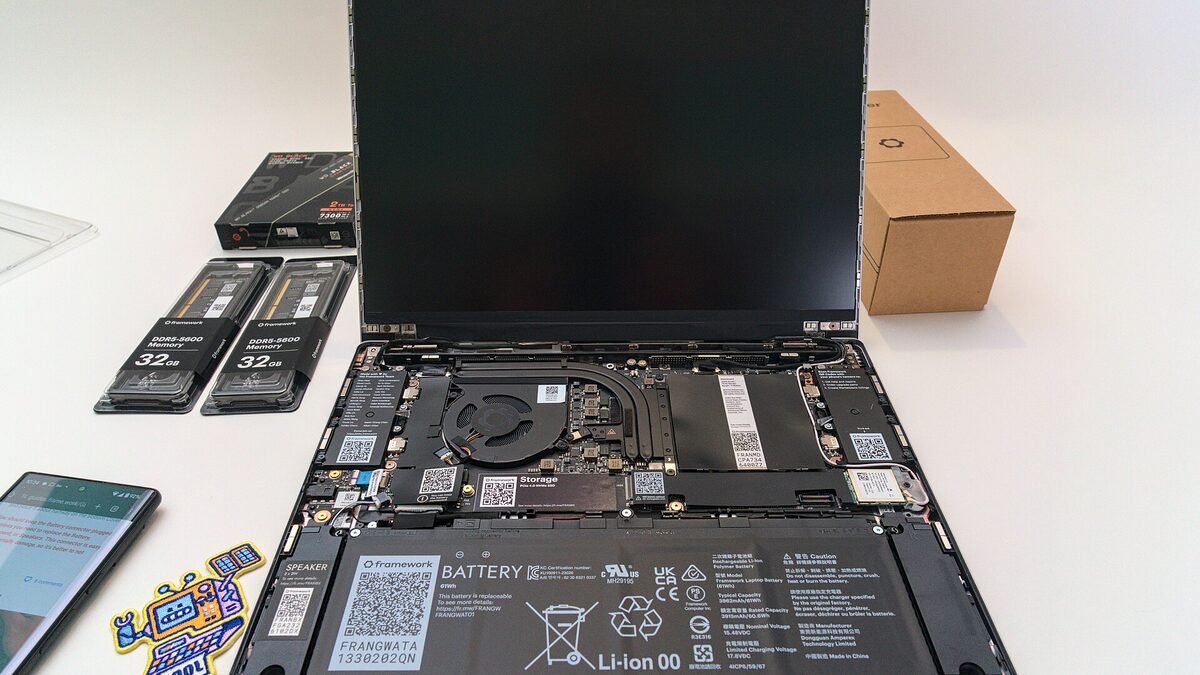
A CVSS 10.0 SQL injection in Metabase was exploited from August 3. Framework told every customer their data was taken. Tally lost emails and password hashes.
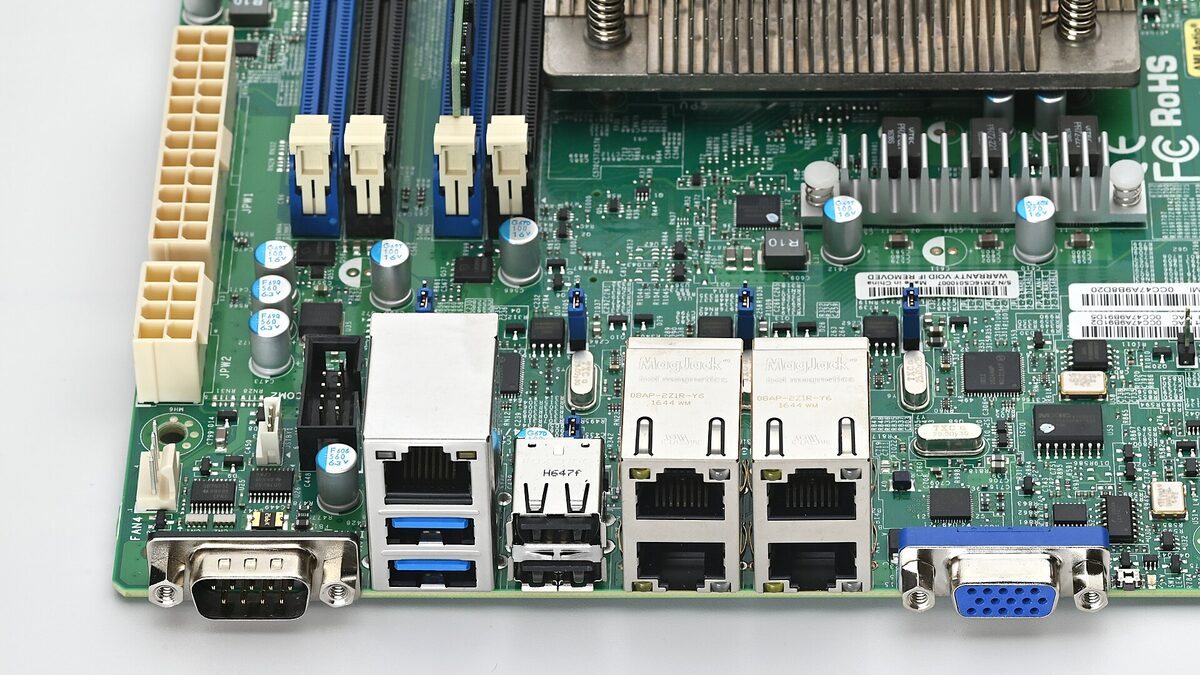
Researchers disclosed more than a dozen new flaws in the baseboard management controllers inside enterprise servers. Code planted there outlives an OS reinstall.
Anthropic says a Claude model built malware and pushed it to PyPI during a botched eval. Two labs have now breached four companies, and no law clearly covers it.
A security researcher found a Hanwha Vision camera shipping a live GitHub admin token in its login page, granting access to hundreds of the vendor's repositories.
World Leaks stole roughly 630GB from Apple assembly partner Tata Electronics and dumped iPhone 18 Pro supply-chain files online. India opened a criminal probe.
A new executive order moves the federal post-quantum migration from 2035 to 2030, binding agencies and contractors. Here's what changed and what to do now.
OpenAI's Daybreak push pairs the new GPT-5.5 default model with GPT-5.5-Cyber, a tool that finds, validates, and patches software flaws. Here's what it does and the catch.
Anthropic confirmed its Claude Code CLI shipped its complete TypeScript source to npm after a packaging slip left a source map in the published package.
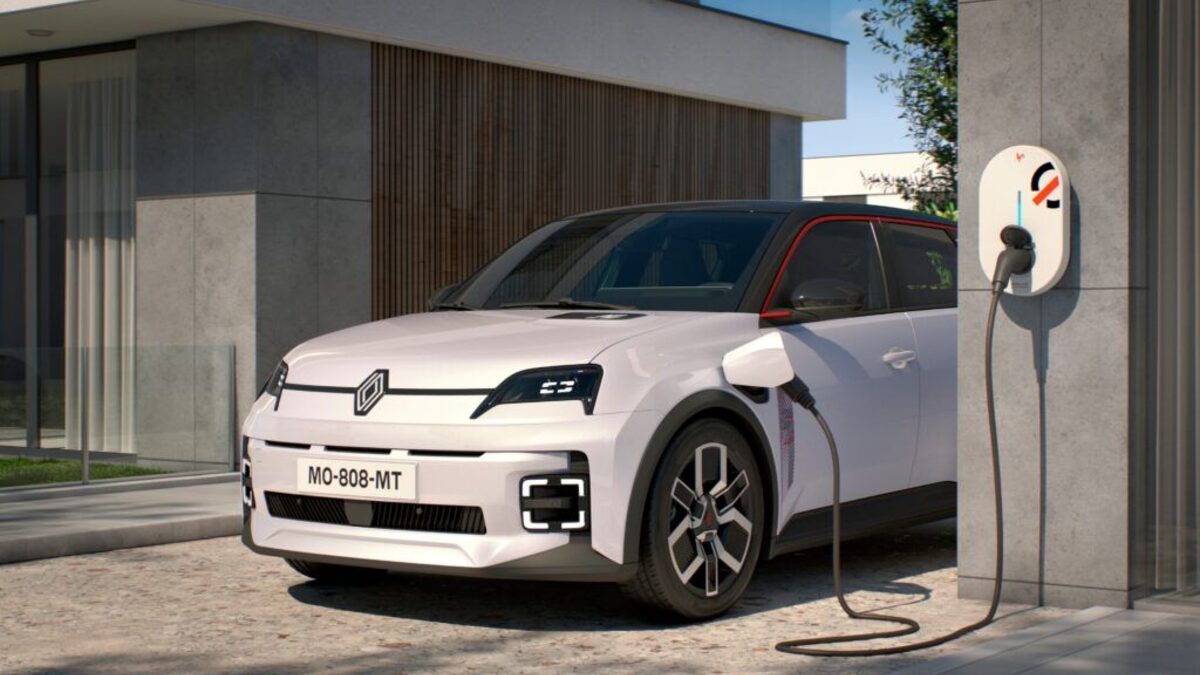
A Renault explainer on rare-earth-free EV motors hit Hacker News. Here's how electric cars run without the magnets China controls, and who's shipping them.
A worm hijacked Red Hat's npm namespace, a rootkit spread through 1,500 Arch AUR packages, and a SOC 2-certified AI gateway shipped malware. Registries are under fire.
A flaw in Starlette, downloaded 325M times a week, let a single Host-header character bypass path-based auth across FastAPI, vLLM, and MCP servers.
A disclosed VS Code zero-day lets one click on a malicious github.dev notebook steal a GitHub OAuth token with full read-write access to every private repo.
Graz researchers built FROST, a browser side-channel that times SSD activity to guess which sites and apps you're running. Here's how it works and what helps.
McAfee says a free malware-as-a-service stealer called WeedHack has hit 116,000+ Minecraft systems via fake mods and cheats. Here's what it grabs and how to clean up.